StratOps Cyber Bootcamp
The method that aligns strategy and operations for cyber experts.
Learn proven approaches to optimize cybersecurity, align it with compliance and convince leadership.
6 live sessions (10 hours) + 15 daily challenges by email
- Focus on what really matters
- Demonstrate the effectiveness of your cybersecurity recommendations
- Accelerate the execution of your actions
€699 excl. VAT
Next bootcamp
September 5 - September 23, 2025
Limited places - Only a few days left to register.






A method born from the field, designed for leaders
From banking to industry, including a period as a reserve officer, Sylvan has led demanding missions in high-pressure environments. He designed the StratOps method to offer leaders clear, actionable and resilient cyber governance in the face of threats.
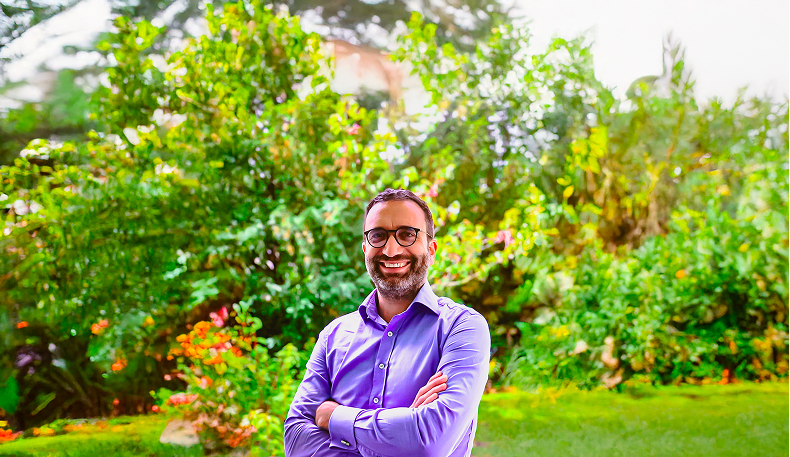
Sylvan Ravinet
Cybersecurity and compliance expert for over 25 years. He supports SMEs and large groups in their regulatory transformation and operational resilience.
He intervenes to:
- Strengthen alignment between leaders, IT and business teams
- Structure evidence and deliverables for audits (ISO 27001, DORA, GDPR…)
- Drive cybersecurity as a strategic lever, not just a compliance obligation


Cybersecurity, risk management and compliance are fragmented, reactive and poorly aligned with business and IT strategies.
Leadership pain points.
- Too many regulations, lack of agility in compliance
- Decision cycles too long in crisis context
- Security measures and controls disconnected from business challenges
- Lack of confidence in the value of cyber frameworks
- Unclear responsibilities... until the leader is held accountable
Operational frictions
- Too many standards, documents, not enough execution consistency
- Duplication of efforts, audit overload, unclear responsibilities
- Gap between business priorities and cyber remediation
- Bottlenecks in control implementation
Executives, CIOs, CISOs, GRC managers... You're not alone in navigating blind.
The StratOps.io method is designed for those experiencing growing tension between strategic requirements, cyber risks and execution capacity:
Executives, founders, auditors
who want to know where their real risk lies, and where to engage their responsibility.
IT Leaders
who want to structure action beyond audits or Excel matrices.
Cyber / GRC Experts
seeking a clear method to drive high-stakes remediation.
StratOps Bootcamp
6 Masterclasses with Sylvan Ravinet covering the 12 capabilities of the StratOps framework
Week 1
May 5—May 9
Understand how to articulate ICT governance and risk management as a lever for compliance and performance. This session provides a robust methodological foundation to ensure strategic board alignment, role consistency in the three lines of defense model.
🗓 Monday, May 5 | 11am-1pm
Objectifs pédagogiques :
Governance
- Recognize the strategic place of cybersecurity in corporate governance.
- Require clear reporting on security posture.
- Arbitrate security priorities from synthetic data.
ICT Risk Framework
- Define relevant digital risk tolerance levels for your organization.
- Request a readable synthesis of the digital risk management framework.
- Question the consideration of digital risks in strategic decisions.
Understand how to articulate ICT governance and risk management as a lever for compliance and performance. This session provides a robust methodological foundation to ensure strategic board alignment, role consistency in the three lines of defense model.
🗓 Monday, May 5 | 11am-1pm
Objectifs pédagogiques :
Governance
- Recognize the strategic place of cybersecurity in corporate governance.
- Require clear reporting on security posture.
- Arbitrate security priorities from synthetic data.
ICT Risk Framework
- Define relevant digital risk tolerance levels for your organization.
- Request a readable synthesis of the digital risk management framework.
- Question the consideration of digital risks in strategic decisions.
Week 2
May 12—May 16
Understand how to articulate ICT governance and risk management as a lever for compliance and performance. This session provides a robust methodological foundation to ensure strategic board alignment, role consistency in the three lines of defense model.
🗓 Monday, May 5 | 11am-1pm
Objectifs pédagogiques :
Governance
- Recognize the strategic place of cybersecurity in corporate governance.
- Require clear reporting on security posture.
- Arbitrate security priorities from synthetic data.
ICT Risk Framework
- Define relevant digital risk tolerance levels for your organization.
- Request a readable synthesis of the digital risk management framework.
- Question the consideration of digital risks in strategic decisions.
Understand how to articulate ICT governance and risk management as a lever for compliance and performance. This session provides a robust methodological foundation to ensure strategic board alignment, role consistency in the three lines of defense model.
🗓 Monday, May 5 | 11am-1pm
Objectifs pédagogiques :
Governance
- Recognize the strategic place of cybersecurity in corporate governance.
- Require clear reporting on security posture.
- Arbitrate security priorities from synthetic data.
ICT Risk Framework
- Define relevant digital risk tolerance levels for your organization.
- Request a readable synthesis of the digital risk management framework.
- Question the consideration of digital risks in strategic decisions.
Week 3
May 16—May 23
Understand how to articulate ICT governance and risk management as a lever for compliance and performance. This session provides a robust methodological foundation to ensure strategic board alignment, role consistency in the three lines of defense model.
🗓 Monday, May 5 | 11am-1pm
Objectifs pédagogiques :
Governance
- Recognize the strategic place of cybersecurity in corporate governance.
- Require clear reporting on security posture.
- Arbitrate security priorities from synthetic data.
ICT Risk Framework
- Define relevant digital risk tolerance levels for your organization.
- Request a readable synthesis of the digital risk management framework.
- Question the consideration of digital risks in strategic decisions.
Understand how to articulate ICT governance and risk management as a lever for compliance and performance. This session provides a robust methodological foundation to ensure strategic board alignment, role consistency in the three lines of defense model.
🗓 Monday, May 5 | 11am-1pm
Objectifs pédagogiques :
Governance
- Recognize the strategic place of cybersecurity in corporate governance.
- Require clear reporting on security posture.
- Arbitrate security priorities from synthetic data.
ICT Risk Framework
- Define relevant digital risk tolerance levels for your organization.
- Request a readable synthesis of the digital risk management framework.
- Question the consideration of digital risks in strategic decisions.

15 days of daily challenges received by email (30 min / day)
Each day, you receive an action to implement:
- Security policy template to adapt
- Governance, risk management or incident response checklist
- Stakeholder communication exercise
By joining the Bootcamp, you unlock:

6 live masterclasses with Sylvan Ravinet

15 daily challenges received by email

40 security policy templates

Video course on BIA (Business Impact Analysis)

Lifetime access to course materials

Direct access to instructor

Private peer community
FAQs
Réponses aux questions fréquemment posées
La notion d'approche proportionnée (présente dans DORA, NIS2, RGPD…) est une exigence, mais reste floue dans son application. StratOps en fait une réalité opérationnelle, à travers : une cartographie BIA des activités critiques, une analyse croisée entre risques cyber, exigences légales, et dépendances numériques, une priorisation des actions fondée sur l'impact métier et la continuité, une mise en œuvre cadencée, selon la maturité et les capacités de l'organisation, une sécurité et une conformité alignées sur les enjeux réels, pas sur une illusion de contrôle.
Nous partons de la réalité opérationnelle, pas des grilles de conformité. Nous remettons les dirigeants en position de commandement, pas de réaction. Nous livrons des preuves concrètes de résilience, utilisables devant un conseil d'administration ou un régulateur. Nous intégrons un accompagnement juridique, via nos cabinets partenaires. Nous fournissons des outils, des copilotes IA et des playbooks intelligents, pas des documents à signer. En bref, nous fournissons une méthode vivante, alignée sur les vrais enjeux.
Que vous ayez besoin d'un diagnostic stratégique ou d'un accompagnement long terme, nous restons disponibles comme : vCISO fractionné / conseiller de confiance, Architecte cyber et conformité (indépendant des vendeurs), Interface avec vos prestataires (MSSP, pentesters, outils), Référent pour cadrer les choix avec la responsabilité du dirigeant en ligne de mire
Le cycle OODA (Observer, Orienter, Décider, Agir) n'est pas nouveau dans l'univers cyber. Les équipes de réponse à incident (CSIRT) l'utilisent déjà pour réagir vite en situation de crise. Ce que StratOps apporte, c'est un changement d'échelle. Nous appliquons la boucle OODA au niveau stratégique — pour aider les dirigeants à garder la main, aligner les arbitrages avec les réalités opérationnelles, et piloter l'ensemble de leur posture cyber avec clarté. Celui qui observe mieux, oriente plus vite, décide plus clairement et agit plus tôt… prend l'avantage. C'est vrai dans un cockpit. C'est vital dans un comité de direction.