The method that gives executives back control over their cybersecurity
A clear approach to align strategy, operations, and compliance—no longer subject to regulatory pressure, audits, or incidents.
Assess in 3 minutes






In cybersecurity and compliance, many companies face a real fog
Executive pain points
- Too many regulations, lack of agility in compliance
- Decision cycles too long in crisis context
- Security measures and controls disconnected from business issues
- Lack of confidence in the value of cyber systems
- Unclear responsibilities... until the executive is held accountable
Operational frictions
- Too many standards, too many documents, not enough execution consistency
- Duplication of efforts, audit overload, unclear responsibilities
- Gap between business priorities and cyber remediation
- Bottlenecks in control implementation
Evaluate your cyber resilience capability
Answer 5 questions. In less than 2 minutes, you'll know:
- Where you stand on the 4 phases of the OODA cycle
- The risks that expose you the most
- The right lever to regain the initiative
La nouvelle responsabilité légale des dirigeants
Les textes comme le RGPD, NIS2 ou DORA ne laissent plus place au doute : les dirigeants sont légalement responsables de la gouvernance des risques cyber, de la résilience opérationnelle, et des décisions liées à la cybersécurité.
Executives, CIOs, CISOs, GRC managers… You're not alone in navigating blindly.
Executives, founders, auditors
who want to know where their real risk lies and where to engage their responsibility.
IT Leaders
who want to structure action beyond audits or Excel matrices.
Cyber / GRC Experts
seeking a clear method to manage high-stakes remediation.
The StratOps promise: regain control and maintain cyber advantage
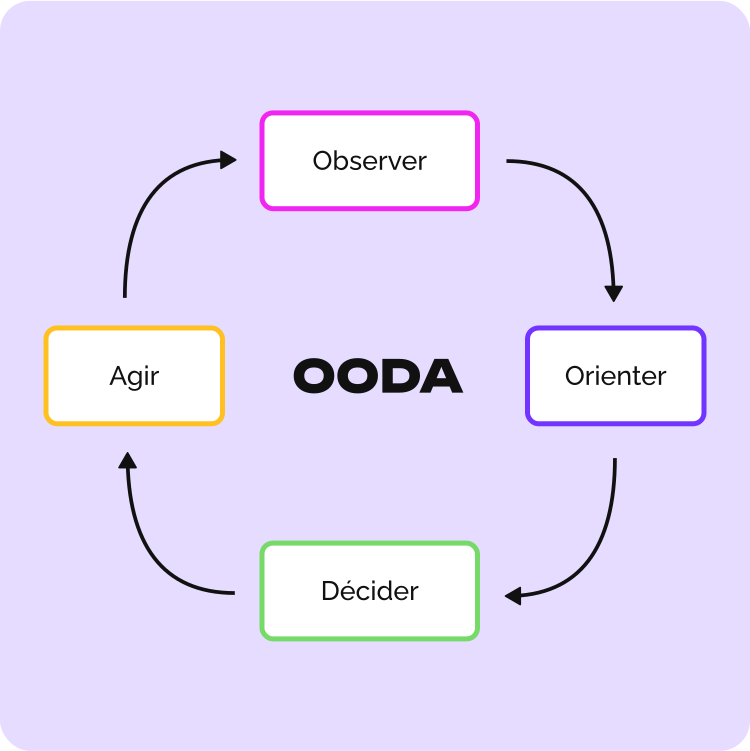
Inspired by the military OODA cycle (Observe, Orient, Decide, Act), our method helps you:
- Observe weak signals - not just incidents
- Orient choices based on ground reality - not an abstract grid
- Decide faster - with clear trade-offs
- Act with concrete evidence - auditable and useful.
No rigid plans: an agile posture, tailored for a changing world.
Result: dynamic, clear cybersecurity manageable by leadership. You no longer endure. You keep the initiative.
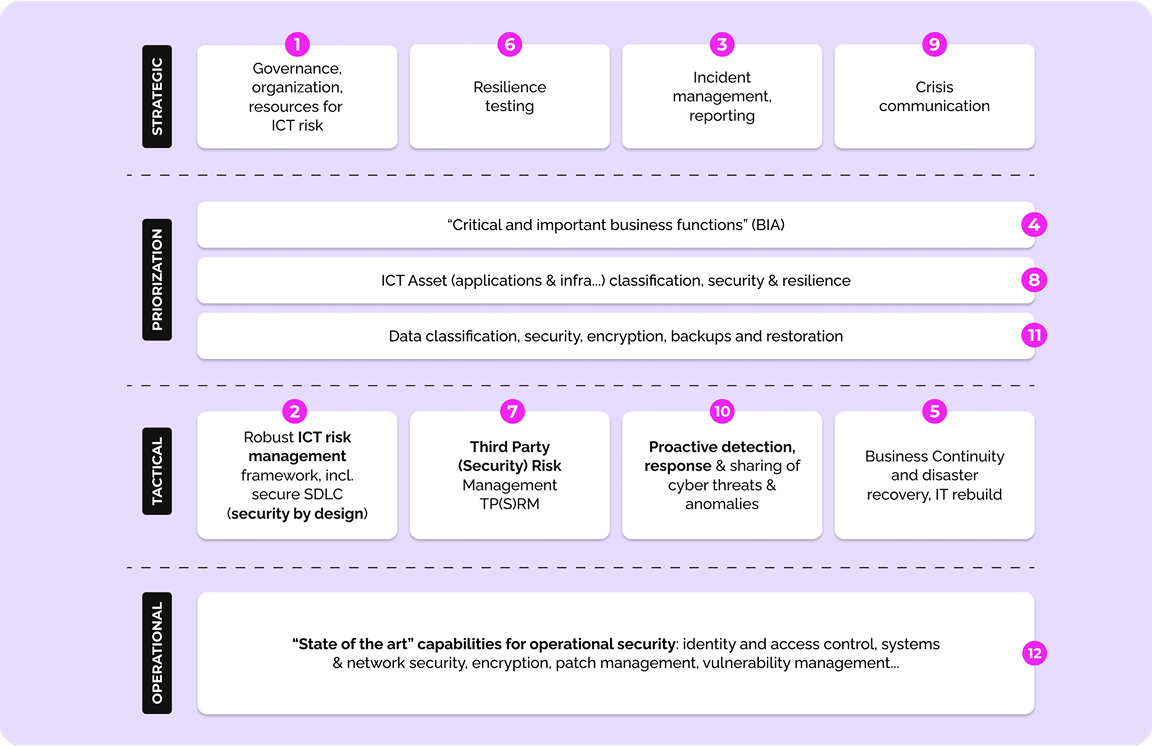
The 12 StratOps capabilities: a clear, manageable, and actionable framework
StratOps structures 12 key cyber resilience capabilities in a unified execution model that aligns strategy, governance, IT, security, and compliance.
Each capability is designed to be:
- Readable: understandable by executives, not reserved for experts
- Defensible: solid in front of an auditor
- Actionable: useful in the field and against attacks, not just on paper
Each capability progresses through four maturity levels:
- Ad hoc: addressed occasionally, without clear structure
- Formalized: documented, but little deployed
- Operational: integrated, measured, managed in processes
- Maneuverable: adjustable in real-time according to context, weak signals, or a crisis
The StratOps objective: progressively advance each capability toward maneuverability - the level where your cybersecurity becomes a strategic and operational advantage, not a burden.
Receive the complete PDF method sheet + 12 detailed capabilities.
Get the methodWhat you may have already tried
Move from fog to cyber maneuverability
Identify your starting point, choose a pack, regain the advantage.
Set a new course with Stratops
FAQs
Answers to frequently asked questions
The notion of proportionate approach (present in DORA, NIS2, GDPR…) is a requirement, but remains vague in its application. StratOps makes it an operational reality, through: a BIA mapping of critical activities, a cross-analysis between cyber risks, legal requirements, and digital dependencies, action prioritization based on business impact and continuity, phased implementation according to organizational maturity and capabilities, security and compliance aligned with real issues, not an illusion of control.
We start from operational reality, not compliance grids. We put executives back in command position, not reaction. We deliver concrete evidence of resilience, usable before a board or regulator. We integrate legal support via our partner firms. We provide tools, AI copilots, and smart playbooks, not documents to sign. In short, we provide a living method, aligned with real issues.
Whether you need a strategic diagnostic or long-term support, we remain available as: fractional vCISO / trusted advisor, Cyber and compliance architect (independent of vendors), Interface with your providers (MSSP, pentesters, tools), Reference point to frame choices with executive responsibility in mind
The OODA cycle (Observe, Orient, Decide, Act) is not new in cyber. Incident response teams (CSIRT) already use it to react quickly in crisis. What StratOps brings is a change of scale. We apply the OODA loop at the strategic level—to help executives keep control, align decisions with operational realities, and manage their entire cyber posture with clarity. Whoever observes better, orients faster, decides more clearly and acts earlier… gains the advantage. It's true in a cockpit. It's vital in a management committee.