Keep the upper hand in cyberspace
StratOps mobilizes a circle of carefully selected internal and external experts. To drive or co-pilot your cybersecurity with clarity, efficiency and executive impact.
A method born from the field, designed for leaders
From banking to industry, including a period as a reserve officer, Sylvan has led demanding missions in high-pressure environments. He designed the StratOps method to offer leaders clear, actionable and resilient cyber governance in the face of threats.
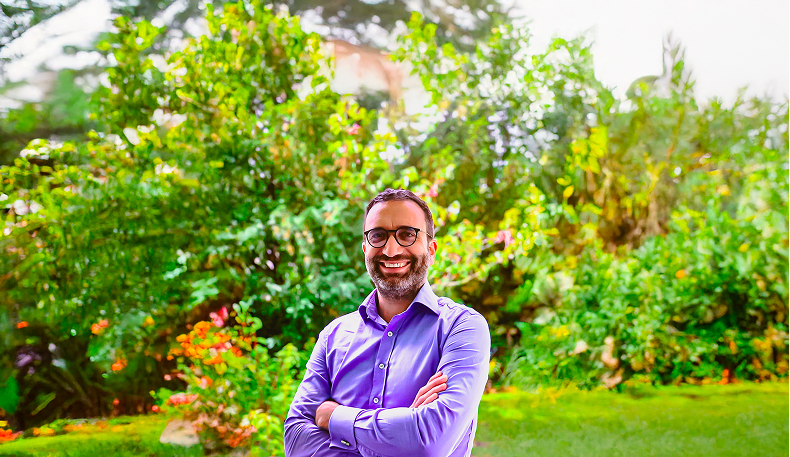
Sylvan Ravinet
Cybersecurity and compliance expert for over 25 years. He supports SMEs and large groups in their regulatory transformation and operational resilience.
He intervenes to:
- Strengthen alignment between leaders, IT and business teams
- Structure evidence and deliverables for audits (ISO 27001, DORA, GDPR…)
- Drive cybersecurity as a strategic lever, not just a compliance obligation


Cyber experts by your side
StratOps activates a small circle of internal and external experts to help you make a breakthrough or secure a capability.
Governance and strategy

Outsourced cybersecurity manager
Becomes your operational security reference (vCISO) with structured reporting.

StratOps Project Manager
Drives your cyber program with method and clarity, from scoping to execution.

Specialized lawyer
Secures your contracts, legal risk analyses and regulatory obligations (GDPR, REC, DORA, NIS2, CRA, AI Act…)

Awareness and training expert
Designs and delivers training adapted to your challenges: EXCO, business, IT, providers. Strengthens collective reflexes and vigilance.

HR Expert
Supports maturity growth through awareness, processes, governance, recruitment and integrates with workforce planning.

Data protection expert
Classifies your critical assets (data, business, systems), secures access, transfers and exposures. Strengthens long-term data protection (encryption, access policy, usage).
Risk, Compliance & Audit

GRC, compliance and audit expert
Prepares, structures and supports your ISO 27001, NIS2, DORA, GDPR audits.

BCP/DRP Expert
Structures your business continuity, emergency and recovery plans.

Cyber and compliance software vendor
StratOps relies on a small circle of proven vendors to accelerate evidence structuring, frameworks and controls, and to support cyber operations (vulnerability management...).
Operations & Tooling
PAM (Privileged Access Management) Expert
Locks down sensitive access, limits privileges, structures critical authorizations. Deploys a pragmatic least privilege approach, without harming operational efficiency.

IAM/IAG Expert
Clarifies access, permissions, sensitive accounts, critical roles, onboarding, mover, offboarding processes, reconciliation, recertification, etc. and configurations

Trusted MSSP
Integrates alerts, managed services and monitoring with clear coordination for operational MTTD, MTTA, MTTR management.

Cyber solution integrator
Deploys validated solutions with efficiency and pragmatism. Drives technical integration (EDR, SIEM, MFA, PAM...) in a framework aligned with your priorities and budget.

Cloud & SaaS security expert
Maps cloud usage (IaaS/SaaS). Identifies configuration and access risks. Implements realistic guardrails, adapted to your business, vendors and workflows.

AppSec/DevSecOps Expert
Integrates security into the software lifecycle. Automates code, dependency and secret controls. Helps your teams code faster… without sacrificing security.
You stay in command with reliable allies
They worked with these companies
StratOps mobilizes them for you







Driving cybersecurity is not about following standards. Or just reacting in crisis. It's about anticipating, adapting, resisting and deciding under pressure. As a team.
Sylvan Ravinet
Founder of StratOps
They testify
Achievements
Here are some examples of StratOps interventions, from vCISO management to strategic board support.
Outsourced cybersecurity management (vCISO)
Défis :
- Scale cybersecurity operations to match company's rapid growth
- Ensure compliance with international financial regulations and industry standards
- Secure complex, multi-cloud and legacy infrastructures
- Build and lead a diverse, high-performing security team
Réalisations :
- Strategy and roadmap approved by Executive Committee.
- PCI DSS 2025 renewal secured through internal efforts and partnerships.
- The 8 main cyber risks are identified and presented to the risk committee.
- An accelerated approach for GDPR security and DORA security is defined.
- New suppliers are qualified (SOC assessments, cloud security, etc.).
- Enterprise-wide BCP approach is redefined.
- Supports transition with arrival of new permanent CISO.
Outsourced cyber program management (finance)
Défis :
- Coordinate with multiple stakeholders, including CDOs, CISOs, DPO, Finance and Compliance departments
- Manage large-scale application portfolios (over 500 for GDPR, over 2500 for RUN)
- Align cybersecurity initiatives with complex regulatory requirements (GDPR, DORA)
Réalisations :
- Successful GDPR application security compliance program for 500 applications
- Defined application security approach and procedures for ABC/AIS, GDPR and DORA compliance
- Prepared RUN phase for over 2500 GDPR applications in relation to key stakeholders
- Defined application and infrastructure approach for DORA security compliance program
- Established effective collaboration between cybersecurity, digital, finance, risk and compliance teams for cyber compliance
Customer cybersecurity advisor to operations leadership.
Défis :
- Understand current state of business model and cybersecurity within limited timeframe
- Address complex regulatory requirements (including GDPR) and third-party risk management with simplified approach
Réalisations :
- Achieved high satisfaction score from client
- Received excellent feedback on depth and clarity of report and actionable recommendations
Cyber advisor to CEO and VP Product
Défis :
- Address diverse stakeholder needs from product management, professional services, customer relationship management and data engineering
- Provide practical insights while having knowledge of standards and regulations (including GDPR)
Réalisations :
- Successfully defined cybersecurity strategy and high-level roadmap for the startup
- Defined detailed cybersecurity requirements for product and next MVP iterations
Test your cyber posture
Answer 5 questions. In less than 2 minutes, you'll know:
- Where you stand on the 4 phases of the OODA cycle
- The risks that expose you most
- The right lever to take back initiative
FAQs
Answers to frequently asked questions
Our ecosystem combines internal experts (like our StratOps project managers) and rigorously selected external specialists. All have been chosen for their specialization, field experience and ability to deliver concrete results, whether as independents, vendors or corporate cyber managers.
We activate a small circle of trusted experts, internal and external, already proven on our missions. This allows us to combine agility, specialization and continuity, without depending on an impersonal directory.
Each expert intervenes within the StratOps method framework, with clear objectives, validated formats and a dedicated project manager who remains your main copilot. No silos, no blind subcontracting.
Yes, it's possible. But we always recommend a preliminary flash assessment to ensure the intervention is targeted and consistent with your overall trajectory (strategy, governance, budget).
We don't sell any tools, but have identified and proven effective cyber solutions (EDR, SIEM, GRC, PAM…) that we can integrate into a pragmatic, manageable approach aligned with your priorities.
Absolutely. Our experts work with CIOs as well as business, HR or procurement teams, to anchor cybersecurity in operational realities. It's no longer a siloed topic.
Integration is generally by co-optation or after successful mission, rarely by spontaneous application. We're looking for profiles aligned with our requirement: clarity, impact, service mindset, and strategy-operations consistency.